



Share this
by Charlie Treadwell on Oct 22, 2026, 9:00:00 AM
Quick answer. Build the 2027 cybersecurity budget from your own baseline, then check it against peers: the IANS Research and Artico Search benchmark puts security at 9.9% of the IT budget in 2026, down from 10.9% in 2025, and common planning guidance uses 10% to 15%. Fund AI security, post-quantum cryptography and segmentation as separate, dated lines. Gartner estimates the post-quantum transition at 1% to 5% of the total IT budget through 2030.
What are the enterprise cybersecurity spending trends for 2027?
Market forecasts and budget surveys measure different things. Record the publisher, date and scope beside every figure before it goes into a budget memo.
What is Gartner’s latest forecast for information security spending?
Gartner’s latest forecast, its September 2026 quarterly update, puts worldwide end-user information security spending at $247.5 billion in 2026, up 13.6% in current US dollars and 12.7% in constant currency. It expects growth of 11.2% in constant currency in 2027 and spending of $372.8 billion by 2030. Those figures come from Gartner’s subscription forecast as reported by Software Strategies Blog (October 5, 2026). Gartner’s most recent public press release on the market, dated July 29, 2025, forecast $213.0 billion for 2025 and $239.8 billion for 2026.
| Gartner forecast update | 2026 forecast (USD) | Source |
|---|---|---|
| July 2025 press release | $239.8 billion (+12.5%) | Gartner, July 29, 2025 |
| 4Q25 update | $244.2 billion | Software Strategies Blog, March 24, 2026 |
| 1Q26 update | $246.2 billion | Software Strategies Blog, April 1, 2026 |
| 2Q26 update | $248.2 billion | Software Strategies Blog, July 6, 2026 (corrected October 4) |
| 3Q26 update (published September 24, 2026) | $247.5 billion; 2027 growth 11.2% (constant currency); $372.8 billion by 2030 | Software Strategies Blog, October 5, 2026 |
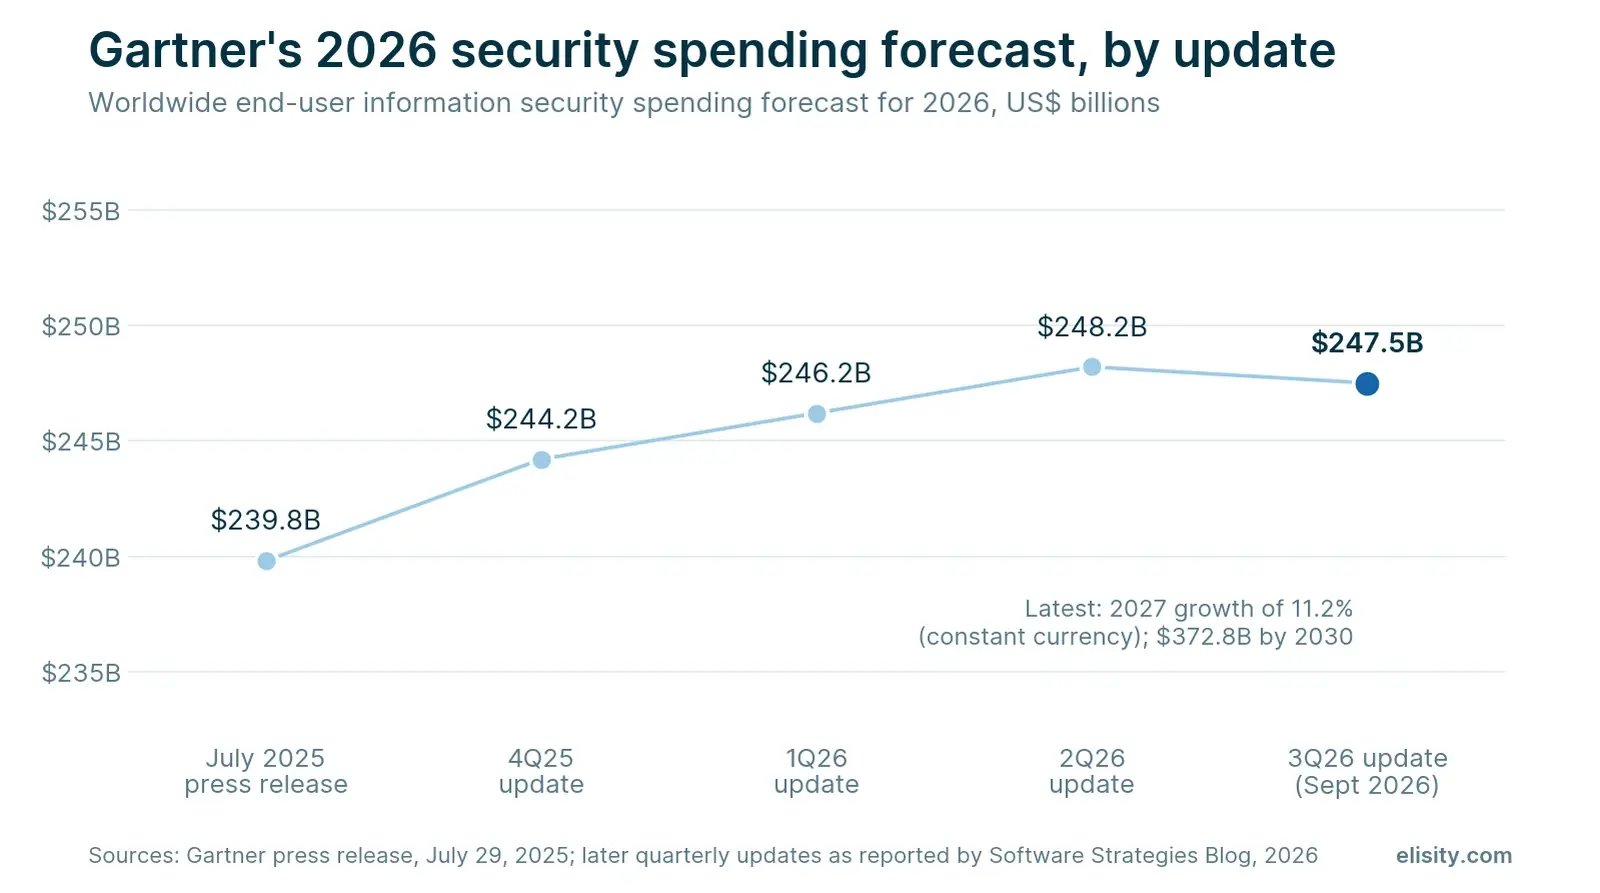
Applying the 11.2% growth rate to the 2026 figure gives roughly $275 billion for 2027. That is arithmetic on a constant-currency rate, not a figure Gartner publishes.
The September update raised one category. Gartner now expects 2027 firewall spending to grow 13.4%, up from 7.8% in June, because price increases and post-quantum readiness are pushing early hardware refreshes; it expects at least 20% of government, financial services and defense customers to upgrade in 2027 (as reported by Software Strategies Blog). The refresh buys PQC key exchange on the VPN and TLS sessions that firewalls terminate. It does not change which internal devices can reach each other.
Gartner’s figure is a market total. It doesn’t include internal headcount. Your budget does.
How does IDC’s forecast differ?
IDC’s Worldwide Security Spending Guide, released March 3, 2026, forecasts about $308 billion in global security spending in 2026, up 11.8%, reaching about $430 billion by 2029. The United States accounts for about $150 billion. The guide spans 38 technology markets, a wider scope than Gartner’s measure, so quote each total with its own scope and never compare the two. IDC’s public release gives no 2027 worldwide total.
What do security and technology leaders expect for 2027?
TechTarget, reporting on the 2026 IANS Research and Artico Search benchmark on September 16, 2026, said median security budget growth was 0% for the second year in a row, average growth was about 5%, and only 45% of budgets grew. Looking ahead, 64% of CISOs in the same study expect an increase in 2027, according to IANS (September 30, 2026).
Forrester’s 2027 Budget Planning Guides (July 15, 2026; more than 2,600 business and technology decision-makers) found that 82% of technology decision-makers expect budgets to rise in 2027, a figure that covers technology budgets broadly. For security specifically, SecurityBrief reported that Forrester’s security and risk guide found 60% of security technology decision-makers expect security budgets to rise 5% or more, and that the guide names post-quantum preparedness and agentic AI frameworks among its priorities. In its 2027 predictions (October 21, 2026), Forrester expects AI to account for 20% of all business technology spend in 2027.
How large is security as a percentage of the IT budget?
No standard sets the share of IT spend that security must receive. The IANS Research and Artico Search benchmark tracks the ratio each year, and it has fallen in each of its last two editions.
| Benchmark | Security share of IT budget | Sample | Timing |
|---|---|---|---|
| IANS / Artico Search 2025 Security Budget Benchmark | 10.9%, down from 11.9% | 587 CISOs | Fielded April 2025; released August 5, 2025 |
| IANS / Artico Search 2026 Security Budget Benchmark | 9.9%, the same level as 2021 | More than 500 CISOs | 2026 edition; survey period not stated on the report page |
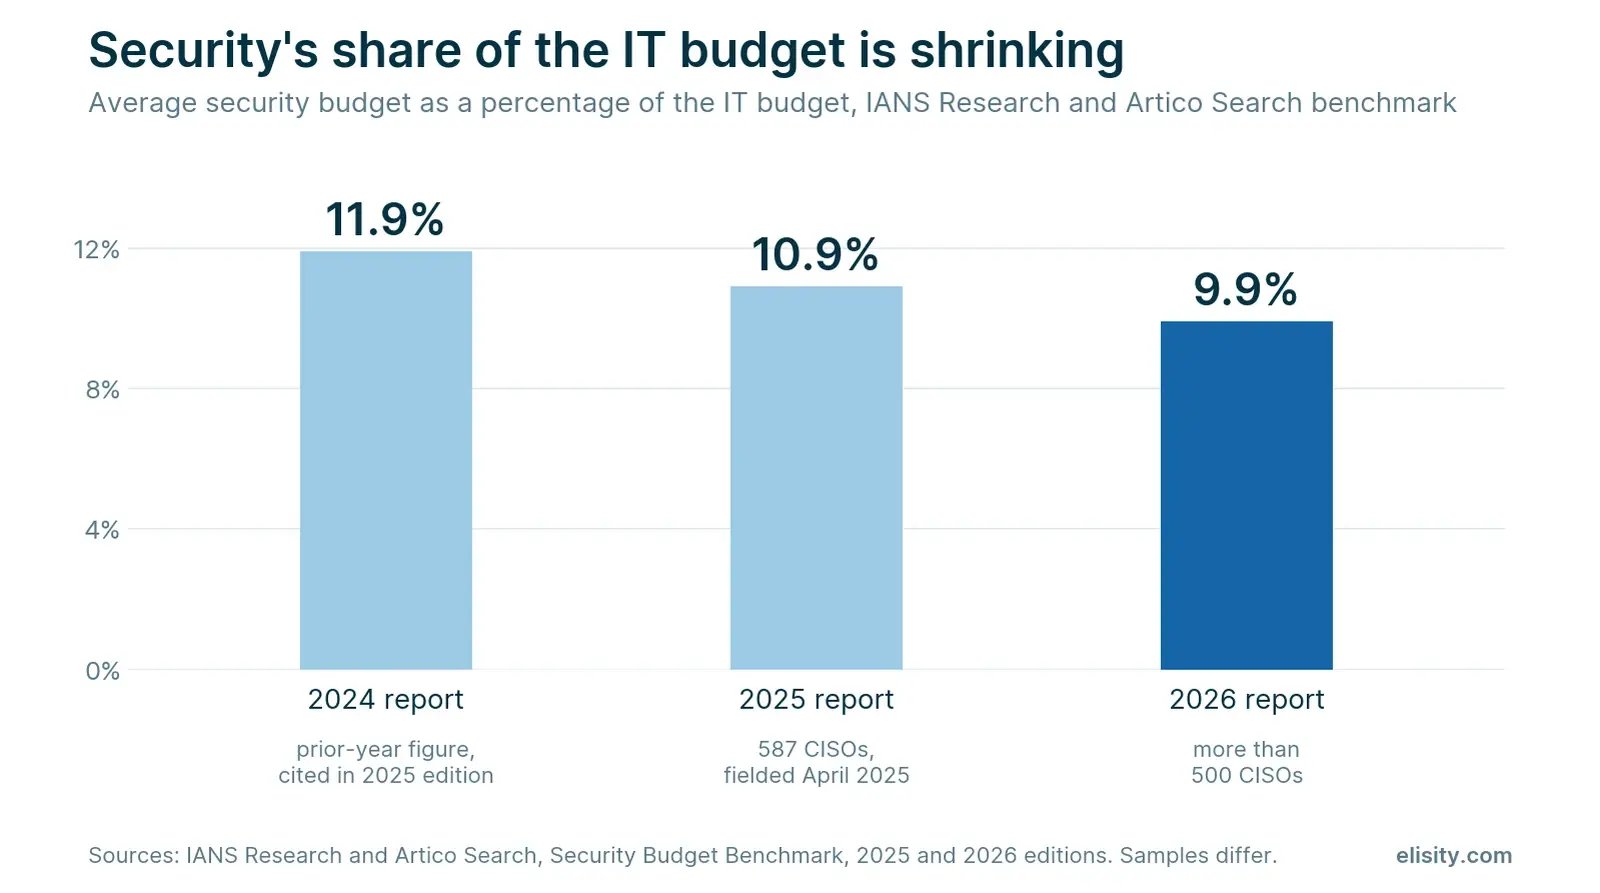
The samples differ, so read the change as a direction rather than a precise trend line.
What percentage of the IT budget do planning guides recommend?
Common planning guidance puts security at 10% to 15% of the IT budget (Huntress, August 12, 2026; itbudgetcalculator.com), and itbudgetcalculator.com suggests 15% to 18% for regulated sectors. These are planning bands, not survey results. The measured average is 9.9%, so a 2027 plan above 10% sits above today’s peer average; justify the gap with obligations and risk, not the band alone.
How does the share change with company size?
Smaller companies spend a far larger share of IT on security. In the IANS 2026 data, companies under $100 million in revenue put 21.6% of IT spend into security, against 7.7% for companies above $10 billion, because a security program carries fixed costs that don’t shrink with the company.
Why does the denominator matter?
A percentage of IT spend is a ratio, so the denominator decides the answer. Before comparing your number with 9.9% or 10.9%, confirm with finance:
- Whether the IT budget includes cloud consumption, OT and systems run outside central IT.
- Whether security staff and managed services sit inside the security budget.
- Whether AI security is funded inside security at all. IANS found that 38% of organizations fund it outside the security budget.
Moving OT networks into the IT budget can lower the security ratio with no change in protection. The same effect explains much of the recent drop: Gartner forecasts worldwide IT spending to grow 14.2% in 2026, to $6.37 trillion (July 27, 2026), faster than security spending, so security’s share of IT falls even when its budget grows.
What is the average cybersecurity budget for a large enterprise?
Benchmarks report large-enterprise budgets as ratios rather than dollar averages, because a dollar average across companies of very different sizes describes none of them. Convert the ratios with your own IT budget and revenue.
| Measure | Figure | Source |
|---|---|---|
| Security share of IT, companies above $10 billion in revenue | 7.7% | IANS, September 14, 2026 |
| Security share of IT, companies under $100 million in revenue | 21.6% | IANS, September 14, 2026 |
| Security share of IT, all sizes | 9.9% (2026); 10.9% (2025) | IANS and Artico Search, 2026; 2025 |
| Security spend as a share of revenue, all sizes | 0.69% average (2025, 587 CISOs) | IANS and Artico Search, 2025 |
As illustrative arithmetic, not a benchmark: a company with a $500 million IT budget at the 7.7% large-company share would spend about $38.5 million on security. The 0.69% revenue figure is an all-size average; large companies tend to sit below it as a share of revenue, so use it as a ceiling check rather than a target.
How do you build a cybersecurity budget for 2027 before comparing it with peers?
Document four inputs before any range goes to finance.
1. What does the current baseline cost?
Inventory the software, infrastructure, people and services already supporting the security program, with renewal dates, integration, training and support costs. Tools that overlap, or that are licensed but not yet operational, are the first place to look for funding.
- Define the assets and business services in scope, including users, devices, workloads and the devices or workloads hosting AI agents.
- Identify required communication paths and high-risk access between asset groups.
- Separate implementation costs from recurring operating costs.
- Name the people who will own policy review, deployment and ongoing maintenance.
2. Which obligations are binding, and which are only proposed?
Maintain a register of applicable laws, contracts, standards and insurer requirements with the compliance or legal team. A proposal, a voluntary framework and a binding obligation are different budget inputs, and a control mapping doesn’t prove compliance. NIST Cybersecurity Framework 2.0 can organize outcomes; it doesn’t prescribe a budget percentage.
3. What headcount does the plan require?
Staff is the largest category in the IANS 2026 data, at 37% of the average security budget. Every new tool needs an owner for policy review and exceptions; price that time at loaded rates.
4. What is new for 2027?
List net-new lines separately from the run rate, each with a one-time cost and a recurring cost. In the IANS 2026 data, AI for security tops the list of net-new funding priorities at 69% of CISOs, followed by security operations automation (51%), zero trust architecture (45%) and identity and access management (39%).
How should a 2027 cybersecurity budget be allocated across categories?
IANS’s public summaries break out three category shares for the average security budget.
| Category | Share of average security budget (IANS / Artico Search 2026) | Note |
|---|---|---|
| Staff | About 37% | Largest single category; software sits two points behind |
| Software, including AI | 35% | Up from 29% in 2025 |
| AI-specific spend | 3% | First year tracked |
| Managed services, testing, training, incident response and insurance | Not itemized in the public summaries | Map each line to a CSF 2.0 function in the next table |
How do budget lines map to NIST CSF 2.0 functions?
NIST CSF 2.0 (CSWP 29, February 26, 2024) organizes security outcomes into six functions: Govern, Identify, Protect, Detect, Respond and Recover. Mapping each budget line to a function shows the board where coverage is thin, which a percentage alone can’t.
| Budget line | CSF 2.0 function | What it typically buys | Cost type |
|---|---|---|---|
| Security leadership, risk and compliance | Govern | CISO office, risk register, policy, obligations register, supplier risk | Recurring |
| Asset inventory and exposure management | Identify | Device and workload discovery, vulnerability management, cryptographic inventory | Recurring |
| Security testing | Identify | Penetration tests, red teaming, control validation and the retest after remediation | One-time and recurring |
| Identity and access management | Protect | MFA, privileged access, identity governance, access for AI agents | Recurring |
| Network segmentation and microsegmentation | Protect | Policy that restricts which assets can communicate, including devices that can’t run an agent; the same policy contains an incident in progress | One-time and recurring |
| Data protection and cryptography | Protect | Encryption, key management, DLP, post-quantum upgrades | One-time and recurring |
| Training and awareness | Protect | Staff training, phishing simulation, administrator certification | Recurring |
| Monitoring and detection | Detect | EDR, SIEM, SOC or MDR service | Recurring |
| Incident response | Respond | IR retainer, forensics, containment playbooks | Recurring |
| Cyber insurance | Govern | Premium, as a risk-transfer decision | Recurring |
| Backup and recovery | Protect and Recover | Immutable backups and backup testing (Protect); restoration and continuity planning (Recover) | Recurring |
What does the arithmetic look like for a $100 million IT budget?
The table applies the two IANS ratios to a $100 million IT budget, then splits each result by the IANS 2026 category shares. This is illustrative arithmetic, not a benchmark; substitute your own IT budget and baseline.
| Line (illustrative arithmetic, not a benchmark) | At 9.9% of IT | At 10.9% of IT |
|---|---|---|
| Security budget | $9.90 million | $10.90 million |
| Staff (about 37%) | $3.66 million | $4.03 million |
| Software, including AI (35%) | $3.47 million | $3.82 million |
| Remainder of the arithmetic (28%) | $2.77 million | $3.05 million |
| Memo line: AI-specific spend (3%) | $0.30 million | $0.33 million |
IANS’s public summaries don’t say whether the 3% AI share sits inside the 35% software share, so it appears as a memo line and is not added to the total. The 28% row is what is left after staff and software; no source measured it as a category.
How should AI security be funded in 2027?
The peer starting point is small. AI accounted for 3% of the average security budget in the IANS 2026 data. For 2027, 69% of CISOs expect AI-related security spend to increase: 45% by 1% to 10% and 24% by more than 10% (IANS, September 30, 2026). Other measures run higher: ISG’s 2026 study (June 30, 2026) found AI-related security exceeds 11% of cybersecurity spending, yet 58% of enterprises call those AI budgets insufficient.
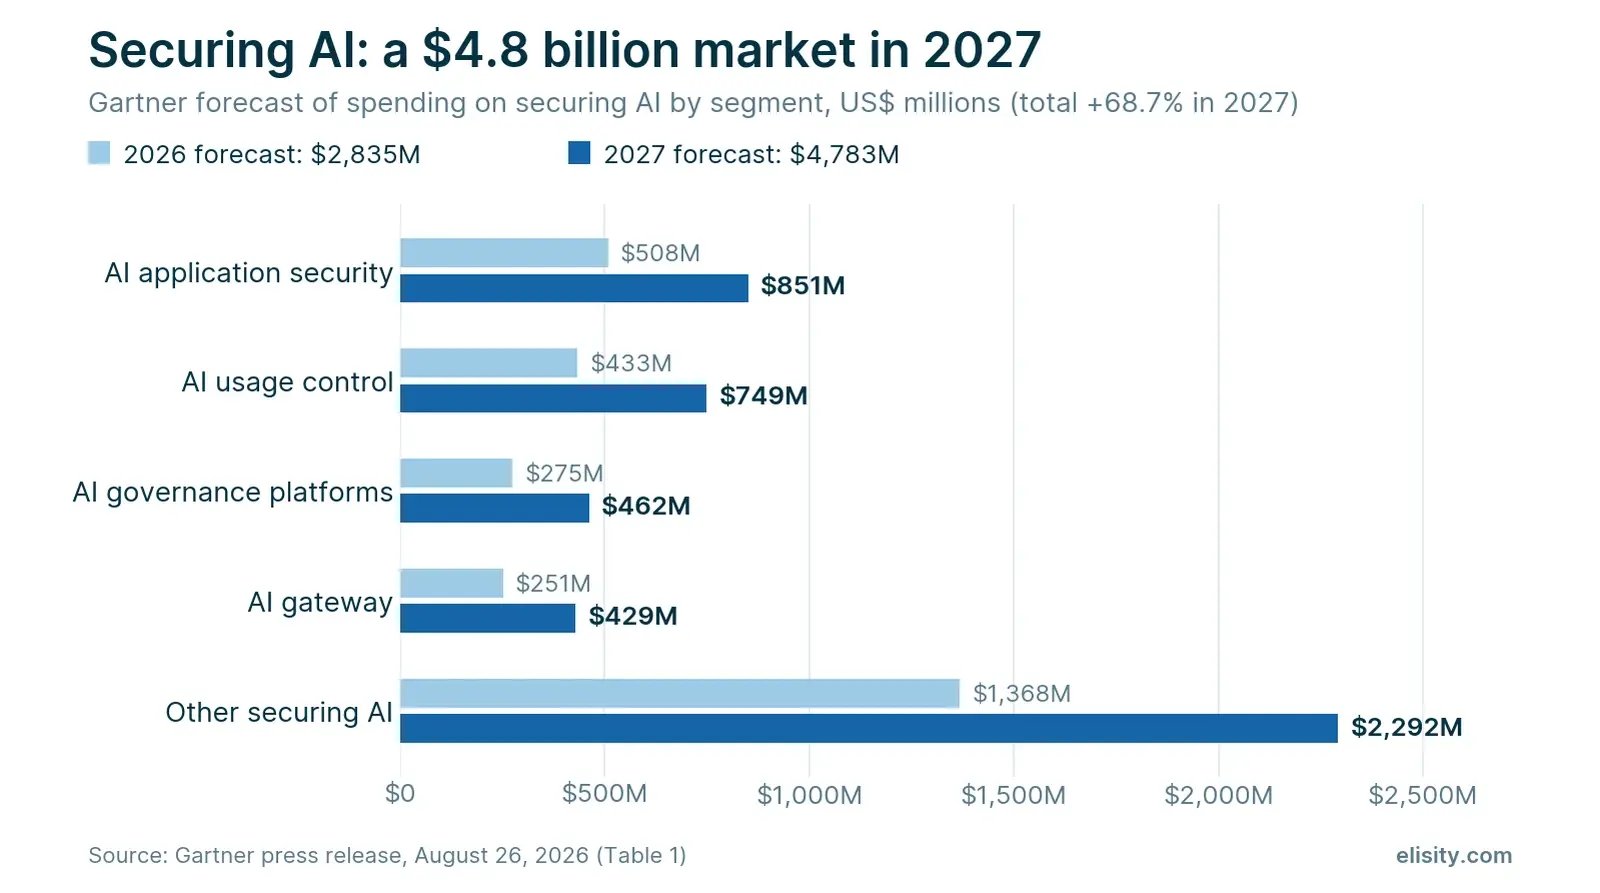
Gartner’s August 26, 2026 forecast puts spending on securing AI at $2.835 billion in 2026, up 83.0%, and $4.783 billion in 2027, up 68.7%, reaching almost $7.7 billion in 2028.
| Gartner securing-AI segment | 2027 forecast (USD) |
|---|---|
| AI application security | $851 million |
| AI usage control | $749 million (+73.0%) |
| AI governance platforms | $462 million |
| AI gateway | $429 million |
| Other | $2,292 million |
| Total securing-AI market | $4,783 million (+68.7%) |
Which budget pays for AI security?
IANS found that 24% of organizations fund AI security as a separate line, 38% embed it in the security budget and 38% fund it outside security. The funding model predicts the outcome: CISOs with a separate AI line raised AI funding about 70% of the time, against 42% when it was embedded and 31% when it sat outside security. Before 2027 approval, name the budget that pays for AI usage control and for access controls around agents, and make it a separate line.
Gartner predicts that by 2029, more than half of successful attacks on AI agents will exploit access-control weaknesses and prompt injection. Include the devices and workloads that host agents in the baseline inventory and in segmentation scope. For the access side of the problem, see how to stop AI agents from becoming over-permissioned.
How should post-quantum cryptography enter the 2027 budget?
Post-quantum cryptography (PQC) belongs in the 2027 budget as a multiyear migration program with its own lines, not a single purchase. The threat that sets the timeline is “harvest now, decrypt later”: an adversary records encrypted traffic today and decrypts it once a cryptographically relevant quantum computer exists. The CISA, NSA and NIST quantum-readiness fact sheet (August 21, 2023) names that threat and puts data that must stay secret for years at the front of the queue.
Gartner puts a size on it. In its September 17, 2026 research on the CISO agenda, Gartner says that “currently Gartner’s best estimate is that this is a multiyear effort between now and 2030, with an expected budget impact between 1% and 5% of the total IT budget.” On a $100 million IT budget, that range is $1 million to $5 million across the program (illustrative arithmetic, not a benchmark). The same research reports that “45% of CISOs say their organization hasn’t begun any PQC-related activities, and another 39% are only in the planning and early testing stages,” and includes the strategic planning assumption that “by 2030, the cost of transitioning to PQC will double for every year an organization delays beginning a coordinated program after 2026.” That is the case for a funded 2027 line rather than a 2028 one. Gartner made the same point publicly on September 30, 2026: organizations that don’t begin piloting PQC by 2027 will face at least 200% higher full-migration costs.
| Total IT budget (illustrative arithmetic, not a benchmark) | At 1% | At 3% | At 5% |
|---|---|---|---|
| $50 million | $0.5 million | $1.5 million | $2.5 million |
| $200 million | $2 million | $6 million | $10 million |
| $1 billion | $10 million | $30 million | $50 million |
The table applies Gartner’s 1% to 5% range to three IT budget sizes as a program total through 2030; spread it across the years of the plan rather than booking it in 2027.
The standards are no longer the blocker. NIST published its first three PQC standards, FIPS 203 (ML-KEM), FIPS 204 (ML-DSA) and FIPS 205 (SLH-DSA), on August 13, 2024. Its draft transition plan, NIST IR 8547 (initial public draft, November 12, 2024), proposes deprecating RSA and elliptic-curve signatures at the 112-bit security level after 2030 and disallowing quantum-vulnerable public-key algorithms after 2035. The UK NCSC timeline (March 20, 2025) sets discovery and planning by 2028, highest-priority migration by 2031 and completion by 2035. In the United States, OMB memo M-26-15 (June 24, 2026) sets federal agencies (the memo excludes National Security Systems) on strategy and discovery in 2026 and 2027, pilots in 2027 and 2028, and migration of key establishment for high-value systems by 2030; for National Security Systems, CNSSP 15, as summarized in NSA’s CNSA 2.0 FAQ (version 2.1, December 2024), requires new acquisitions to be CNSA 2.0 compliant from January 1, 2027 unless otherwise noted. Neither binds a commercial enterprise directly. Suppliers to agencies and to NSS programs will feel those dates first. For 2027, the budget question is how fast you can find quantum-vulnerable cryptography and decide what happens to each instance.
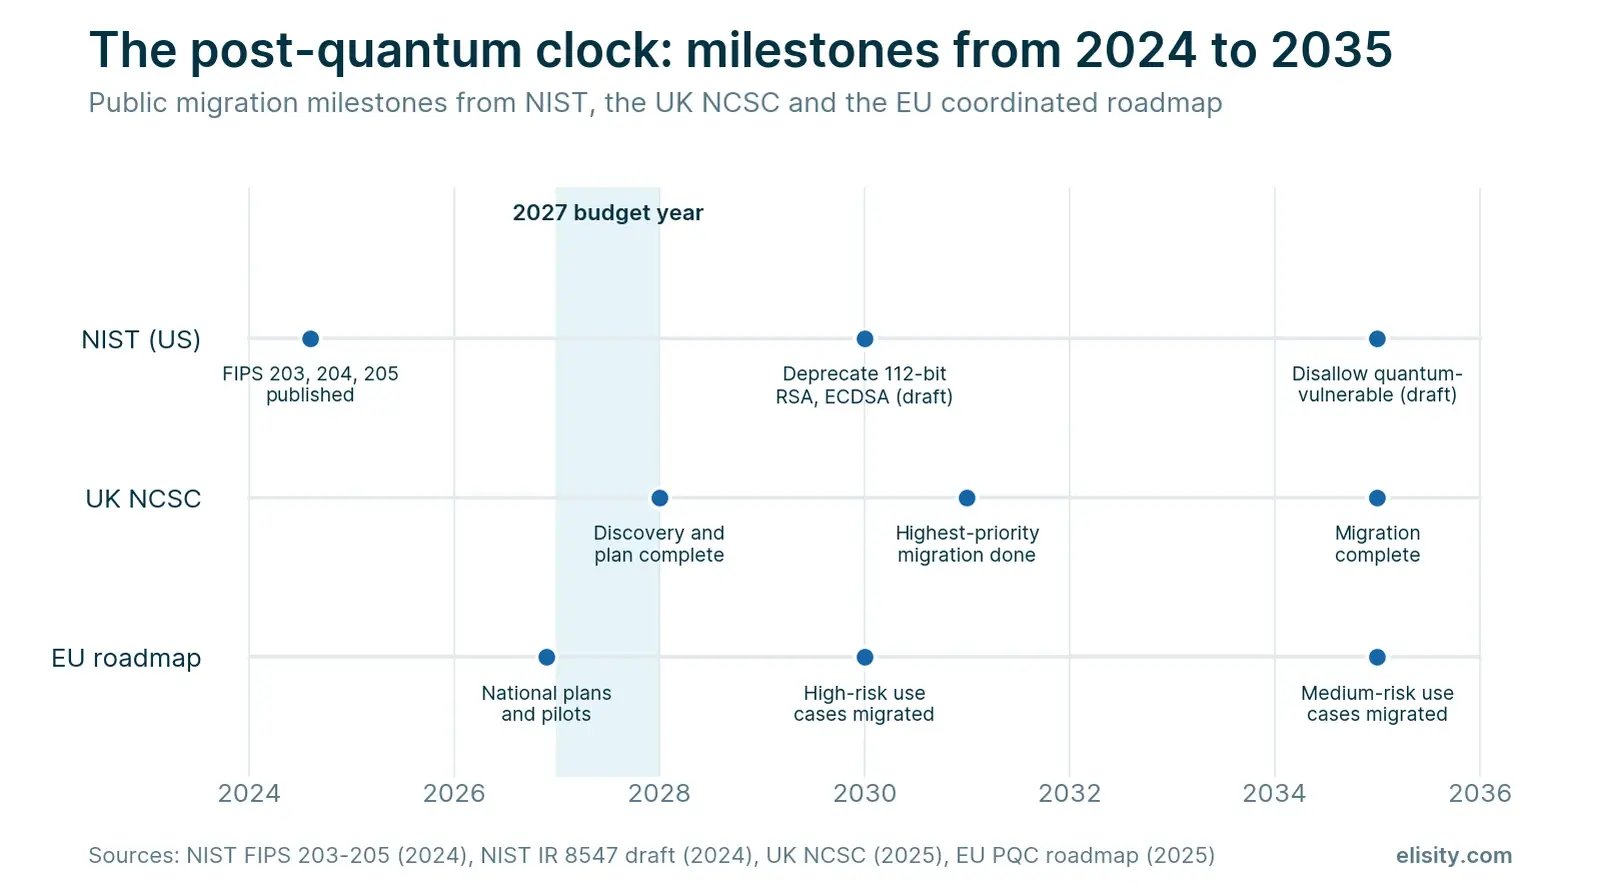
Four steps turn that work into budget lines.
1. Build a cryptographic inventory
Inventory every place public-key cryptography is used: TLS and VPN endpoints, certificates and PKI, code signing, SSH, identity systems, databases, network equipment, and the firmware inside IoT, OT and medical devices. Network scans alone miss keys stored offline, cryptography compiled into applications and dependencies inside supplier products, so combine scanning with endpoint, code and vendor sources. Record more than algorithm and key length: each entry needs a business owner, the systems that depend on it and how long the protected data must stay confidential. Gartner lists “data protected, required confidentiality lifetime and HNDL exposure” among the minimum fields, and describes the inventory as both a cryptographic bill of materials (CBOM) and a migration burn-down tracker. The CISA, NSA and NIST fact sheet lists inventory, risk assessment and vendor engagement as the core of a quantum-readiness roadmap. Treat the inventory as a system you keep current, not a one-time assessment.
2. Score the risk
Rank each finding by what a future decryption would expose, and what a forged signature would let an attacker impersonate or install. Long-lived sensitive data (patient records, intellectual property, regulated financial and government information), externally reachable connections and systems that sign software or firmware rise to the top. A key exchange protecting a short-lived session on an internal test network ranks below one protecting records that must stay confidential for a decade.
3. Identify what can be upgraded
Sort the scored inventory into three paths, each with its own budget line:
- Vendor products: ask each supplier for a dated PQC roadmap, the versions that support ML-KEM and ML-DSA, and the performance impact, then tie upgrades to existing renewal and refresh dates and put the requirement in contracts. CISA’s PQC product categories list (January 23, 2026) says PQC-capable products are widely available for cloud services, messaging, web software and disk encryption, while networking hardware and identity, credential and access management are still transitioning.
- In-house applications: fund refactoring toward crypto-agility, meaning algorithms change through configuration rather than code rewrites, and test hybrid modes, which run a classical and a post-quantum algorithm together, before production.
- Legacy cryptographic debt: systems that cannot support the new algorithms need a replacement, retirement or containment decision with a date.
4. Segment what can’t be upgraded
Some systems will run quantum-vulnerable cryptography for years: medical devices on long certification cycles, PLCs and controllers on production lines, building systems and other embedded devices whose firmware the owner cannot change. CISA’s PQC product categories list leaves OT and IoT out of scope, so for many of these devices there is no federal list of PQC-capable products to buy from. Gartner recommends that CISOs “plan containment or accelerate the retirement of systems that cannot migrate,” using “encapsulation, cryptographic shims or PQC-protected channels only as governed interim measures.” CISA’s post-quantum guidance for OT (October 2024) says entities “should prioritize network segmentation for legacy OT, end-of-life software, and platforms that require extensive time to apply updates.” Network segmentation is one way to contain them. Until those systems are replaced, reduce who can reach them: restrict each one to the communication paths it requires, so a compromised peer cannot reach it except over approved paths enforced at the switch or wireless controller, and record the exception with an owner and a replacement date. Run the policy in simulation first to see what would be blocked before anything is enforced, and keep OT policies static rather than letting them shift automatically. For the options in detail, see how to protect systems that can’t be upgraded to post-quantum cryptography.
Segmentation limits reachability; it does not repair weak cryptography. Traffic on the paths you still permit can be recorded and decrypted later, so pair containment with cutting the sensitive data those systems handle, consider a PQC-capable gateway or tunnel in front of systems whose traffic must stay confidential, and keep the replacement date in the plan.
| PQC budget line | Type | Evidence to collect |
|---|---|---|
| Cryptographic discovery and inventory | One-time and recurring | Tooling quotes, coverage across network, endpoint, code and suppliers, and the staff time to keep it current |
| Governance and program staffing | Recurring | A cryptographic center of excellence (CCoE) with owners for policy, inventory, exceptions and vendor follow-up; hours per quarter |
| Vendor upgrades | Mostly tied to renewals | Supplier roadmaps with dates and versions, mapped to existing refresh and renewal cycles |
| Application refactoring | One-time | Engineering estimates for crypto-agility and hybrid-mode testing per application |
| Containment for systems that can’t migrate | One-time and recurring | Assets in scope, required communication paths, policy maintenance time, replacement dates |
Which regulatory deadlines affect 2027 budgets?
Budget against obligations at the dates they actually apply. Status as of October 22, 2026:
| Obligation | Status on October 22, 2026 | Budget implication |
|---|---|---|
| HIPAA Security Rule update (proposed rule published January 6, 2025) | Still a proposal. The current Security Rule (45 CFR Part 164, Subpart C) applies. HIPAA Journal reported on July 8, 2026 that the regulatory agenda moved the final-action target to July 2027. | Fund risk-based work under the current rule; no final-rule deadline exists yet. |
| CIRCIA final rule | Received at OIRA for review on October 1, 2026. CISA says covered incident and ransom-payment reporting is not required until the final rule takes effect, and gives no target date. | Prepare reporting workflows; confirm scope on publication. |
| CMMC | Advancement to Phase 2 was suspended on July 13, 2026 for a task-force review, according to Holland & Knight (July 31, 2026). No new Phase 2 date had been announced as of mid-October 2026, per ISI. Phase 1 self-assessments, SPRS scores, DFARS 252.204-7012 and NIST SP 800-171 still apply. | Keep Level 2 readiness funded; confirm the assessment level each contract requires. |
| EU Cyber Resilience Act | Manufacturer reporting obligations (24-hour early warning, 72-hour notification) apply from September 11, 2026. Main obligations apply from December 11, 2027. | EU product sellers need 2027 funding for vulnerability handling. |
| OMB M-26-15 post-quantum migration (federal agencies, excluding National Security Systems) | Issued June 24, 2026. Discovery 2026 to 2027, pilots 2027 to 2028, key establishment for high-value systems by 2030, signatures by 2031, full migration by 2035. Systems that can’t support PQC are to be identified and given priority for replacement or decommissioning. Executive Order 14412 also directs a FAR rule on contractor PQC compliance by December 31, 2030. | Vendors selling to agencies should expect PQC questions in 2027 procurement; fund inventory and supplier roadmaps now. |
| CNSA 2.0 (National Security Systems) | New NSS acquisitions must be CNSA 2.0 compliant from January 1, 2027 unless otherwise noted; equipment that can’t support it is to be phased out by the end of 2030. | Applies to NSS and their suppliers, not to commercial enterprises generally. |
For a sector view of incident reporting, see the CIRCIA guide for healthcare.
How do cybersecurity budgets differ by industry?
Public industry budget bands are planning estimates rather than survey results; itbudgetcalculator.com, for example, labels its sector bands as estimates. Company size moves the ratio more than sector does (21.6% of IT under $100 million in revenue against 7.7% above $10 billion, per IANS), so settle these questions before comparing with any sector band.
| Industry | Questions to settle before setting the number |
|---|---|
| Healthcare | How many IoMT and clinical devices cannot run an endpoint agent? Who pays for clinical engineering time during policy changes? |
| Manufacturing | Does the IT budget include OT networks and plant systems? Do Cyber Resilience Act obligations apply to products sold in the EU? |
| Defense industrial base | Which contracts require which CMMC level, and how does the Phase 2 suspension change the timing of assessment spend? |
| Financial services | Which systems are in PCI DSS scope, and would segmentation reduce that scope? Which disclosure obligations would a material incident trigger? |
| Critical infrastructure | Which entities will fall under CIRCIA once the final rule takes effect, and what will reporting workflows cost to run? |
See also industrial cybersecurity budget alignment for manufacturers and healthcare microsegmentation for medical devices.
What does microsegmentation cost, and how do you estimate TCO?
Microsegmentation total cost of ownership (TCO) is the full cost, over a stated period, of restricting which assets can communicate, including the people who maintain policy. License cost is one row. Deployment labor, infrastructure changes, policy review and exception handling are the others.
| TCO line item | Type | Evidence to collect |
|---|---|---|
| Licenses and subscriptions | Recurring | Quotes on the same asset count and term for every option |
| Agents or appliances | One-time and recurring | Agent count by operating system, assets that can’t take an agent, appliance hardware and refresh |
| Infrastructure changes | One-time and recurring | Any switch software license tier the design requires for enforcement (recurring), plus software or hardware upgrades, checked against the supported-models list |
| Control-plane hosting | Recurring | VM or container capacity for any on-premises enforcement controller; ask each vendor for sizing and high-availability design |
| Implementation and integration | One-time | Quoted services, internal labor, identity and CMDB integrations, change windows |
| Policy operations | Recurring | Measured time to review, simulate, approve and maintain policies, plus exception handling; ask what rollback takes (if the design changes network configuration, rollback is a change window; if it only withdraws policy, it is not) |
| Training | One-time and recurring | Hours per administrator and per operations team |
| Coverage | Outcome | Assets observed and assets with verified enforcement, reported separately |
| Security outcome | Outcome | Unnecessary communication paths removed and documented exceptions |
What does network segmentation cost if you keep existing infrastructure?
Reusing existing switches and firewalls takes most new hardware out of the TCO, though not the software license tier or controller hosting, and moves the cost into validation: which models and software versions the design supports, what share of sites run them, and what the unsupported share needs. Ask whether older switches that cannot enforce can still be onboarded for visibility, with enforcement one layer up, to defer refresh cost. Host-agent designs avoid that dependency but add per-host cost and agent lifecycle work, and still need another control for devices that can’t run an agent, including many IoT, OT and medical devices. If a PQC-driven firewall refresh is in the 2027 plan, check how much of today’s rule base is east-west zone traffic that access-layer segmentation could carry instead, then size the refresh for the north-south traffic the firewalls terminate. Internal firewalls pushed to the access layer add east-west rules and the people to operate them.
For enforcement models side by side, see this comparison of microsegmentation vendors and deployment models, and the microsegmentation buyer’s guide and checklist lists evaluation criteria.
Budget for coverage, because intent runs well ahead of it. In an Omdia survey commissioned by Elisity (published April 28, 2026; 352 US security and IT leaders in healthcare and manufacturing at organizations with 1,000 or more employees), 99% said they were implementing or planning microsegmentation, yet only 9% reported that more than 80% of their critical systems were protected. Treat the vendor-commissioned, two-sector result as directional.
How do you justify a cybersecurity budget increase to the board?
Justify the increase with the argument that has worked for peers: board priorities, regulation and business risk, not breach fear. In the IANS 2026 data, budget requests tied to a board focus averaged 23% increases and regulation-driven requests 22%, against 13% for business risk and 9% for breach-driven requests. Among CISOs whose budgets grew, 48% cited business or operational risk and 3% cited a breach.
| Argument behind the budget request | Average increase (IANS 2026) |
|---|---|
| Board focus or priority | 23% |
| Regulation | 22% |
| Business risk | 13% |
| Breach | 9% |
Present the ask as ranked lines, each with the risk it reduces, its cost and its owner, so the board decides where to draw the line. An expected-loss model, such as FAIR, can rank lines by loss reduced per dollar; label its outputs as estimates.
Calculate total cost over a stated period with your own staffing rates, licensing quotes and deployment plan. Distinguish measured savings from estimates, and show how the conclusion changes if implementation takes longer or the supported scope is smaller.
IBM’s 2026 Cost of a Data Breach report, published July 29, 2026, puts the global average breach cost at $4.99 million, up 12%, based on 602 organizations and breaches studied from March 2025 to February 2026. IBM also reports that security AI and automation cut breach costs by $1.93 million on average. It is an average across other organizations, useful as context for a risk discussion. It is neither your expected loss nor a saving.
Label risk scenarios clearly, and avoid promising a fixed reduction in breach cost, a universal payback period or a customer ROI figure without supporting evidence. For metrics to track after approval, see microsegmentation ROI and KPI benchmarks; for a segmentation-specific worksheet, see the microsegmentation budget planning guide.
How should cyber insurance enter the budget?
Ask your insurer or broker which controls and evidence apply to your policy. Segmentation may be relevant to underwriting, but terms vary by insurer and policy. Keep premium savings out of the base case unless a documented quote supports them.
How should the rollout be phased to support the business case?
Start with a defined environment and business owner. Establish visibility, model required access and simulate proposed policies against observed traffic. As general practice, resolve exceptions with application owners before administrators approve enforcement, then fund the next phase from measured results.
Where does segmentation fit in the budget?
Segmentation can be funded from the zero trust architecture line, which 45% of CISOs named as a net-new priority in the IANS 2026 data. Elisity supports a phased rollout by correlating identity and security context in IdentityGraph and enforcing approved policies through supported network infrastructure. Elisity does not require a software agent on the IoT, OT and medical devices it protects, which matters because those devices often cannot be upgraded to post-quantum cryptography. Elisity enforces allow-or-deny policy at the network edge; it does not decrypt or alter traffic. Validate infrastructure support, rollout effort and the scope of the expected outcome during a proof of value.
In October 2026, IonQ announced an agreement to acquire Elisity, with closing expected in the fourth quarter of 2026. Elisity said the next phase would extend IdentityGraph with cryptographic inventory and risk information. Elisity does not inventory cryptography today; that comes from crypto discovery tools and vendor attestations.
Explore the Elisity platform or ask the Elisity Assistant for the solution brief that fits your environment.
What should you take to finance?
- The baseline: current spend by category, renewal dates, and one-time versus recurring costs.
- The ratio check against 9.9% and 10.9%, with your denominator and company size stated, and the 10% to 15% planning band labeled as guidance.
- Net-new 2027 lines, each with an owner, a one-time cost, a run rate and a milestone.
- A named budget home for AI security, preferably a separate line.
- Each line mapped to a CSF 2.0 function, and the ask framed around board priorities, regulation and business risk.
- The obligations register with status dates, separating binding rules from proposals.
- A TCO for each segmentation option on the same scope and period.
- A post-quantum line: inventory first, upgrades tied to renewals, containment for systems that can’t migrate.
Frequently asked questions
How much should a company spend on cybersecurity in 2027?
A company should set its 2027 cybersecurity budget from its own baseline, obligations and staffing, then check it against peers. The IANS Research and Artico Search benchmark puts security at 9.9% of the IT budget in its 2026 report and 10.9% in 2025. For a $100 million IT budget, that arithmetic gives $9.9 million to $10.9 million, which serves as a check on the bottom-up number.
What percentage of the IT budget should go to security?
No standard sets the share of IT spend that security must receive. IANS Research and Artico Search measured security at 10.9% of IT budgets in 2025 (587 CISOs) and 9.9% in 2026 (more than 500 CISOs). Common planning guidance uses 10% to 15%, and smaller companies spend a larger share (21.6% under $100 million in revenue against 7.7% above $10 billion, per IANS). Before comparing, confirm what finance counts in the IT denominator, including cloud, OT and AI spend.
What is Gartner’s latest forecast for information security spending?
Gartner’s latest forecast, its September 2026 quarterly update, puts worldwide end-user information security spending at $247.5 billion in 2026, with 11.2% constant-currency growth expected in 2027 and $372.8 billion by 2030, as reported by Software Strategies Blog. Gartner’s latest public press release, from July 29, 2025, forecast $239.8 billion for 2026.
How should a security budget be allocated across categories?
In the IANS Research and Artico Search 2026 benchmark, staff accounted for 37% of the average security budget and software including AI for 35%, up from 29% in 2025. AI-specific spend was 3% in its first year tracked. Use those shares to compare against your own baseline; they aren’t a required split.
How much of the 2027 budget should go to AI security?
AI security has no settled benchmark share yet. AI was 3% of the average security budget in the IANS 2026 data, and 69% of CISOs expect AI-related security spend to rise in 2027. Gartner forecasts the securing-AI market at $4.783 billion in 2027, up 68.7%. Decide first whether AI security is funded inside or outside the security budget.
How should you estimate microsegmentation TCO?
Estimate microsegmentation TCO over a stated period and the same asset scope for every option. Include licenses, agents or appliances, infrastructure changes, deployment labor, integration, training and ongoing policy maintenance. Report verified enforcement coverage separately, and don’t count estimated avoided losses as realized returns.
How should post-quantum cryptography fit in a 2027 security budget?
Post-quantum cryptography fits in a 2027 security budget as a multiyear program that starts with a cryptographic inventory. Score findings by how long the protected data must stay confidential, upgrade vendor products and applications as PQC support arrives, and restrict network reachability for systems that cannot be upgraded until they are replaced. Gartner estimates the transition as a multiyear effort through 2030 with a budget impact of 1% to 5% of the total IT budget.
How do you justify a cybersecurity budget increase to the board?
Justify a cybersecurity budget increase to the board with board priorities, regulation and business risk rather than breach fear. In the IANS 2026 data, board-driven requests averaged 23% increases and regulation-driven requests 22%, against 9% for breach-driven requests. Present ranked lines with the risk each reduces, its cost and its owner, and label any loss estimates as estimates.
Is the proposed HIPAA Security Rule update binding?
No. As of October 22, 2026, the HIPAA Security Rule update published as a proposed rule on January 6, 2025 hasn’t been finalized, and the current Security Rule still applies. HIPAA Journal reported in July 2026 that the regulatory agenda targets final action for July 2027. Budget for risk-based work under the current rule and track HHS for final dates.
Sources
- Gartner, Forecasts Worldwide End-User Spending on Information Security, July 29, 2025
- Gartner, Forecasts the Market for Securing AI, August 26, 2026
- IDC, Worldwide Security Spending Guide, March 3, 2026
- Software Strategies Blog (Louis Columbus), Gartner 3Q26 information security forecast, October 5, 2026
- Software Strategies Blog, Gartner 2Q26 information security forecast, July 6, 2026 (corrected October 4, 2026)
- Software Strategies Blog, Gartner 1Q26 forecast, April 1, 2026
- Software Strategies Blog, Gartner 4Q25 forecast, March 24, 2026
- Gartner, Forecast: Information Security, Worldwide, 3Q26 Update (abstract), September 24, 2026
- Gartner, Worldwide IT spending forecast, July 27, 2026
- Gartner, Top five actions for CISOs to take by end of 2026, September 30, 2026
- IANS and Artico Search, 2026 Security Budget Benchmark report page
- IANS and Artico Search, 2025 Security Budget Benchmark report page
- IANS, Security budgets stall as AI reshapes 2027 spending, September 14, 2026
- Huntress, Guide to cybersecurity budget planning, August 12, 2026
- itbudgetcalculator.com, Cybersecurity budget planning bands, updated August 25, 2026
- ISG, 2026 cybersecurity study (Business Wire), June 30, 2026
- Forrester, 2027 technology and security predictions, October 21, 2026
- IBM, Cost of a Data Breach 2026 report page
- NIST, CSWP 29, The NIST Cybersecurity Framework (CSF) 2.0, February 26, 2024
- OMB, M-26-15, Execution of the Migration to Post-Quantum Cryptography, June 24, 2026
- NSA, CNSA 2.0 and Quantum Computing FAQ, version 2.1, December 2024
- CISA, Post-Quantum Considerations for Operational Technology, October 2024
- IANS and Artico Search, 2025 Security Budget Benchmark, August 5, 2025
- IANS and Artico Search, 2026 Security Budget Benchmark, 2026
- IANS, AI and 2027 security budgets, September 30, 2026
- TechTarget, coverage of the 2026 IANS benchmark, September 16, 2026
- Forrester, 2027 Budget Planning Guides release (via Yahoo Finance), July 15, 2026
- SecurityBrief, coverage of Forrester’s 2027 security budget guide, July 2026
- IBM, Cost of a Data Breach 2026, July 29, 2026
- CISA, CIRCIA page, accessed October 22, 2026
- OIRA, CIRCIA final rule review, received October 1, 2026
- HHS, HIPAA Security Rule proposed rule, January 6, 2025
- HIPAA Journal, Security Rule update postponed, July 8, 2026
- Holland & Knight, CMMC Phase II suspension, July 31, 2026
- ISI, CMMC compliance status, reviewed October 19, 2026
- Hunton Andrews Kurth, Cyber Resilience Act reporting obligations, September 11, 2026
- Omdia survey commissioned by Elisity, April 28, 2026
- NIST, Cybersecurity Framework 2.0, February 26, 2024
- CISA, NSA and NIST, Quantum-Readiness: Migration to Post-Quantum Cryptography, August 21, 2023
- NIST, FIPS 203, 204 and 205 post-quantum standards, August 13, 2024
- NIST, IR 8547 Transition to Post-Quantum Cryptography Standards (initial public draft), November 12, 2024
- UK NCSC, Timelines for migration to post-quantum cryptography, March 20, 2025
- European Commission, Coordinated implementation roadmap for the transition to post-quantum cryptography, June 2025
- CISA, Product categories for technologies that use post-quantum cryptography standards, January 23, 2026
- IonQ, IonQ to acquire Elisity, October 12, 2026
- Gartner, “CISO Agenda Priority: Transition to Postquantum Cryptography Before It’s Too Late (And Too Expensive),” Mark Horvath, Sarah Almond, Thomas Lintemuth, 17 September 2026
Gartner, Hype Cycle, and Cool Vendors are trademarks of Gartner, Inc. and/or its affiliates. Gartner does not endorse any company, vendor, product or service depicted in its publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner publications consist of the opinions of Gartner’s business and technology insights organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this publication, including any warranties of merchantability or fitness for a particular purpose.
Share this
Get the latest on microsegmentation, Zero Trust, and network security delivered to your inbox.
No Comments Yet
Let us know what you think